Why Mobile App Protection Goes Beyond the Perimeter

Mobile app protection means securing the app itself, not just the servers it connects to. Start by testing code before release, protecting sensitive data and API access, and making the app harder to reverse engineer or alter. Then add runtime checks that can detect tampering, debugging, or a compromised device while the app is in use.
A phone is outside your control once someone installs your app. That makes client-side defenses important, but they should work alongside secure backend services and regular updates. The goal is to make attacks harder without making the app slower or frustrating people who use it.
As director of product at Synergy Labs, I'll walk through how to build those layers into a practical security plan.
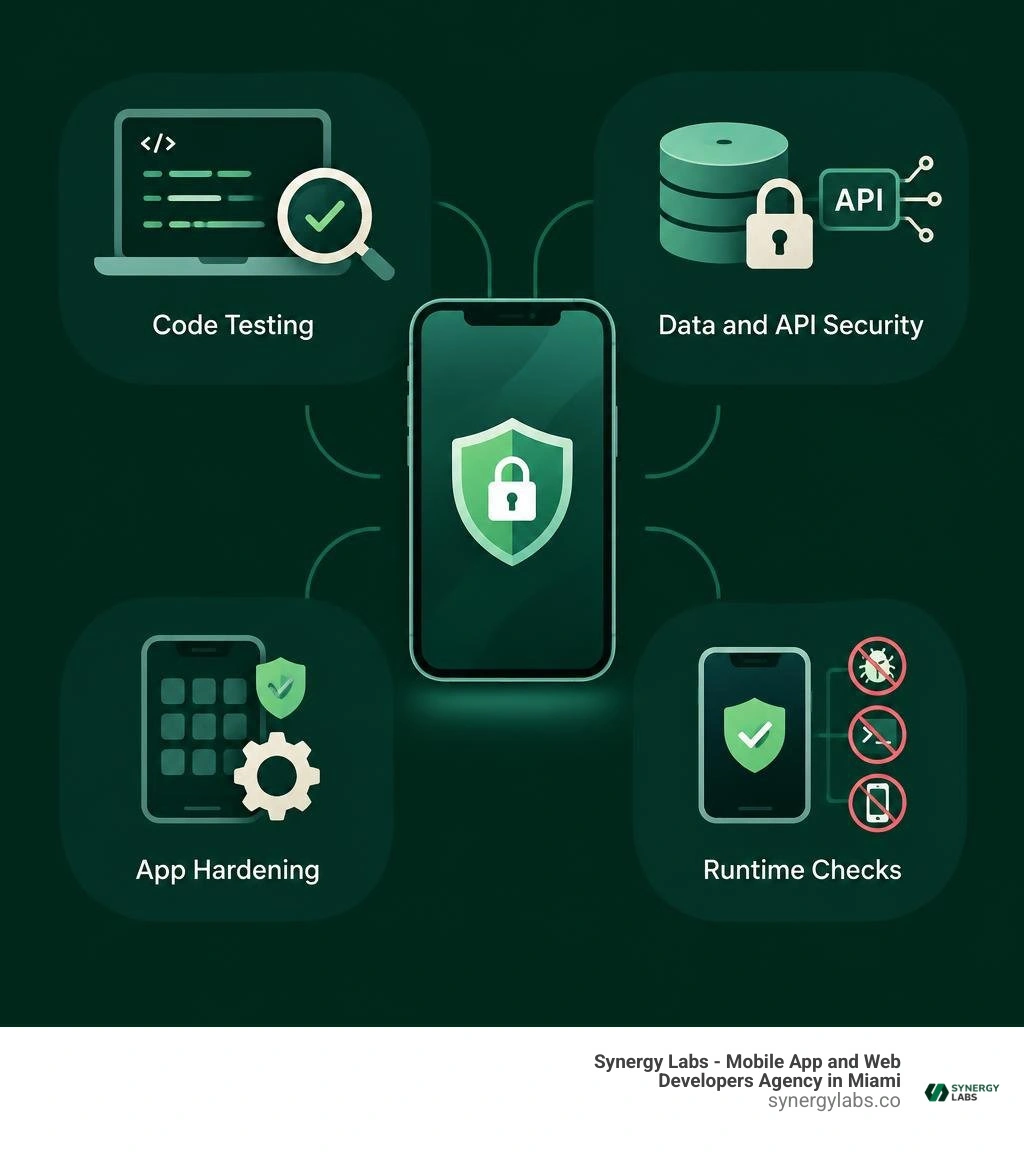
Basic mobile app protection terms:
The Evolving Mobile Threat Landscape and Attack Vectors
The mobile ecosystem operates on a scale that was unimaginable a decade ago. With more than 3.8 billion mobile app users worldwide, apps have become the primary digital touchpoint for everything from personal banking to critical enterprise operations. By the end of 2023, mobile app revenues reached $935 billion, and user appetite shows no sign of slowing down, with global app downloads hitting nearly 288 billion in 2024.
However, this massive adoption brings extraordinary risk. Unlike traditional web applications where critical business logic remains safely behind fortified cloud firewalls, mobile applications distribute compiled code directly into untrusted client environments. When an end user downloads your application, your binary sits on physical hardware that you do not own, manage, or monitor.
In hostile hands, that binary can be decompiled, analyzed, modified, and redistributed within hours. Attackers extract hardcoded secrets, decrypt API keys, map internal endpoints, and manipulate client-side logic to bypass billing models or authentication checks. Building resilient digital products demands understanding how to secure mobile apps against persistent local tampering and automated reverse engineering.
Threat Vectors: Jailbreaking, Rooting, and Dynamic Hooking
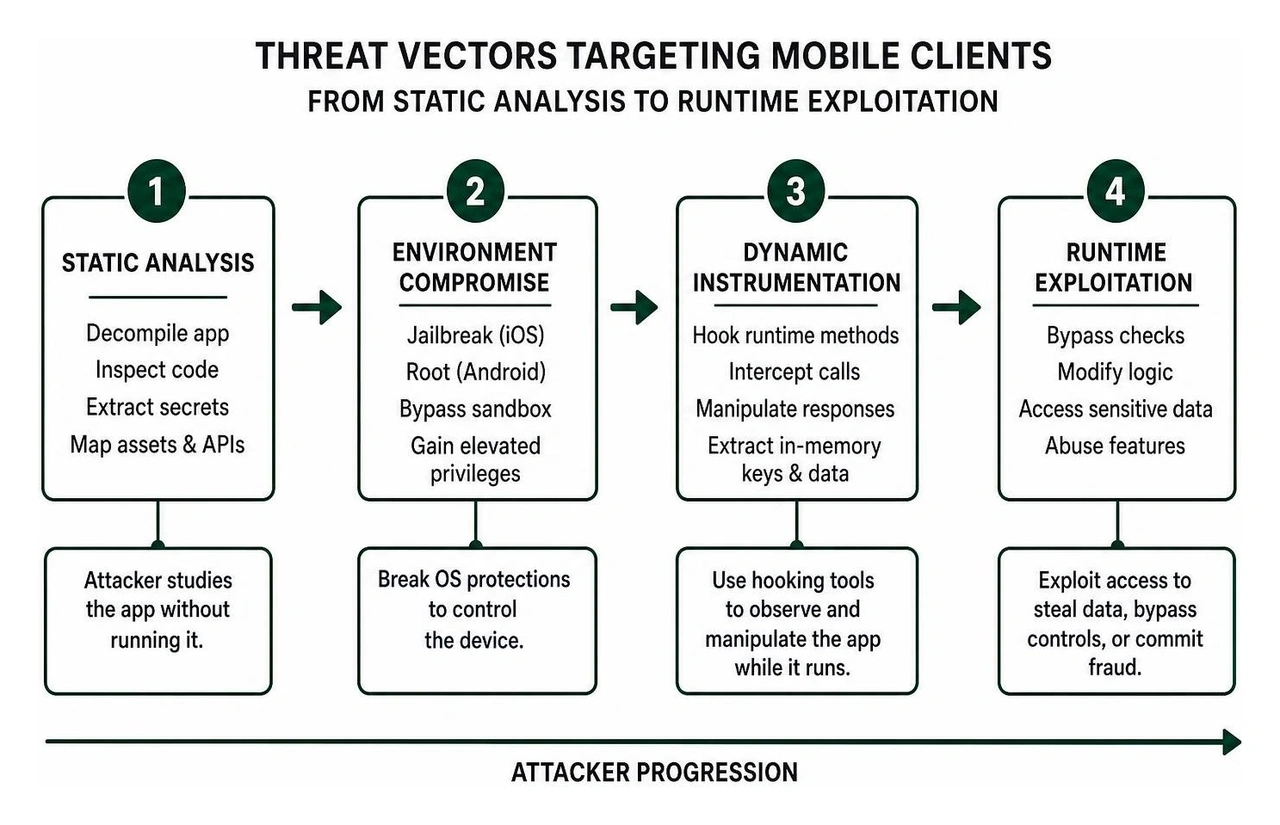
Attackers rely on dynamic and static vectors to probe mobile software. When a mobile operating system is rooted (on Android) or jailbroken (on iOS), the sandbox designed to isolate apps from one another is dismantled. This compromise grants administrative privileges to unauthorized utilities, allowing malicious actors to inspect runtime memory, hook critical functions, and bypass standard cryptographic protections.
Dynamic instrumentation frameworks represent the primary weapon for modern mobile exploitation. Attackers deploy dynamic hooking engines to intercept runtime method calls, manipulate return values, and extract in-memory cryptographic keys without modifying the binary on disk. Common threats include:
- Root and Jailbreak Environments: Tools such as Magisk, KernelSU, and checkra1n grant root access while deploying cloaking mechanisms to evade standard detection routines.
- Dynamic Hooking Engines: Frameworks like Frida allow attackers to trace function calls, bypass biometric authentication checks, and tamper with application parameters on the fly.
- Debugger Attachment: Malicious actors attach native debuggers (such as LLDB or GDB) or utilize ptrace injection to pause execution, inspect heap memory, and manipulate logic registers.
- Emulator and Virtualized Sandboxes: Running apps inside headless emulators or dual-space containers lets adversaries automate attacks, simulate synthetic GPS coordinates, and spoof device identifiers.
- Binary Repackaging: Attackers extract legitimate APKs or IPAs, inject malicious payloads or advertising adware, re-sign the binary, and distribute cloned versions to unsuspecting users.
The 2026 Threat Reality: Compressed Breakout Speed and Automated Exploitation
The timeline for mobile security has transformed. In 2026, mobile threat telemetry highlights a dramatic 65% increase in attacker breakout speed. The operational window—the time between an adversary's initial binary compromise or environment probe and the unauthorized exfiltration of sensitive data—has compressed to under 30 minutes.
This velocity is powered by automated de-obfuscation pipelines and artificial intelligence. Threat actors no longer spend weeks manually stepping through disassembled assembly code. Instead, automated de-compilers analyze control flows, identify API interaction points, and strip static defenses instantly.
Because adversaries leverage AI-assisted tools to identify security flaws, relying on static security or backend firewalls is no longer sufficient. Client-side binaries must possess native intelligence capable of actively neutralizing attacks as they occur.
Core Architecture of Modern Mobile App Protection
Building client resilience requires a multi-layered defense architecture. Security cannot exist as an isolated feature added right before release. It must be woven into the compiled code, runtime execution, and enterprise management layer.
A comprehensive architectural blueprint combines deterministic binary hardening, dynamic self-defense, and robust policy governance, as outlined in the enterprise mobile app protection overview.
RASP, Code Obfuscation, and Binary Hardening
Static deterrence and runtime active defense form the twin pillars of client binary protection.
Code obfuscation transforms human-readable source code into an intricate maze without altering its functionality. Advanced binary hardening techniques include:
- Control Flow Flattening: Rewriting conditional logic and loops into complex, flat switch statements controlled by state variables, breaking decompilers.
- Dynamic Symbol and String Encryption: Encrypting sensitive strings, class names, method descriptors, and API URLs so they remain unreadable in static disassemblers and are only decrypted in memory during brief execution windows.
- Instruction Pattern Polymorphism: Modifying the internal instruction layout across unique builds so that an adversary who manages to map out one version must restart their reverse-engineering efforts from scratch upon the next update.
While obfuscation increases the cost and time required for reverse engineering, Runtime Application Self-Protection (RASP) actively defends the running process. RASP acts as a deterministic digital immune system embedded directly within the application binary.
RASP continuously monitors for signs of hooking frameworks, ptrace attachment, emulator execution, and memory tampering. When a threat is detected, RASP executes pre-programmed countermeasures: terminating the app session, clearing cached tokens from memory, wiping local cryptographic keys, and dispatching live threat signals back to central security operations.
App Protection Policies and MAM in Enterprise Zero Trust
Securing consumer apps requires defending against external threat actors, whereas enterprise software must also prevent insider data leakage across managed and unmanaged personal devices (BYOD). In zero-trust mobile ecosystems, Mobile Application Management (MAM) establishes a secure container around enterprise workflows without requiring invasive full-device management.
Enterprises configure intune app protection policy guidelines to enforce granular client controls:
- Data Containment and DLP: Preventing corporate data from being copied, pasted, or shared into unmanaged personal applications, while restricting local device storage to encrypted enterprise sandboxes.
- UI and Access Restrictions: Blocking screen capture, disabling unauthorized third-party keyboards to prevent keylogging, and requiring dedicated biometric authentication or application-level PINs before granting access.
- Conditional Launch and Selective Wipe: Automatically assessing device health upon cold start and blocking app execution if the operating system is out of date, rooted, or missing required patches. If an employee leaves or a device is reported lost, administrators can perform a selective wipe of business data while leaving personal photos and files intact.
Deployment Models and Implementation Strategies
Selecting the right deployment architecture determines how cleanly security integrates into your development lifecycle, user experience, and ongoing maintenance workflows.
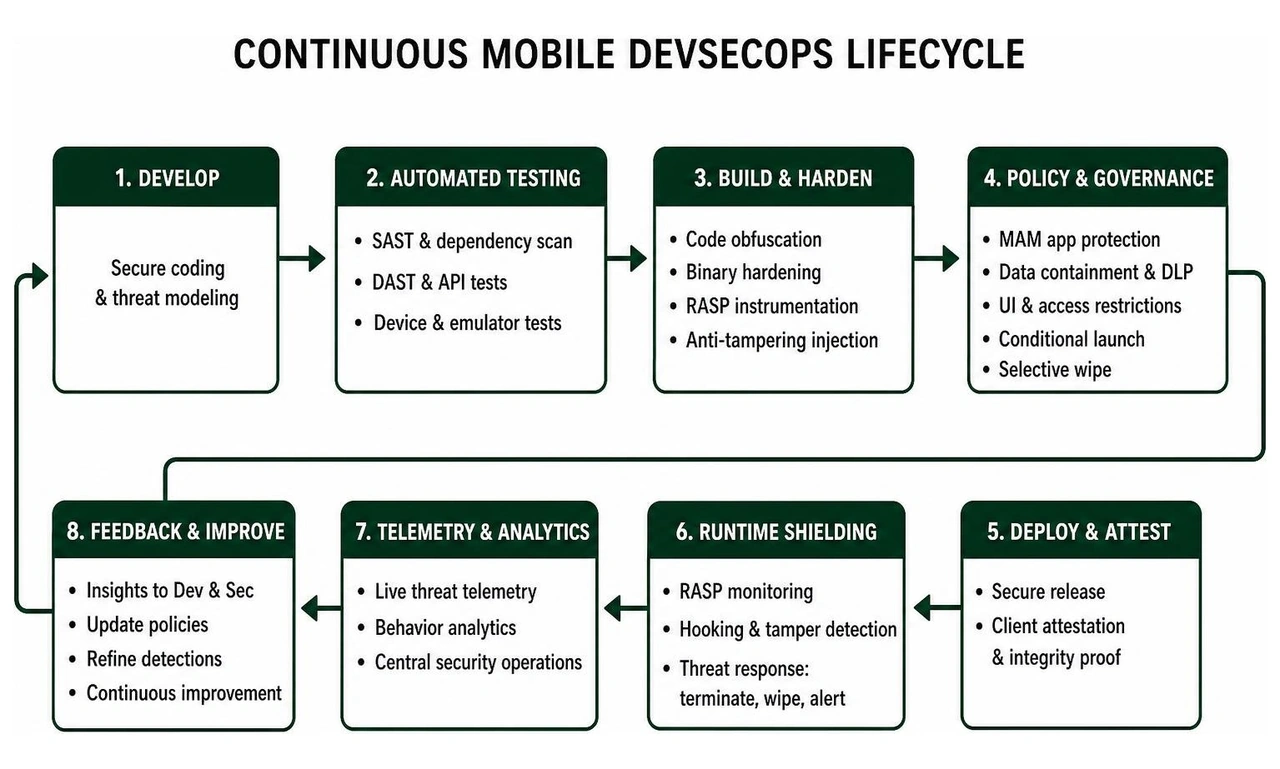
Engineering teams evaluate three primary integration models, balancing implementation effort with security granularity as part of their strategic mobile app security practices:
- SDK-Based Integration: Developers import native libraries directly into the codebase and manually invoke security checks. This grants fine-grained programmatic control over how the app responds to individual threats, though it requires developer overhead and ongoing code refactoring.
- No-Code Post-Compile Hardening: The application is built normally, and the resulting binary (APK, AAB, or IPA) is hardened through an automated post-compilation pipeline. Security controls, RASP checks, and anti-tampering logic are injected deterministically into the compiled bytecode before final signing. This decouples security engineering from feature development, allowing teams to harden native, Flutter, or React Native apps in under 60 seconds without writing custom security code.
- Cloud-Based Gateway Shielding: Client-side attestation tokens are evaluated alongside API gateway defenses. The app continuously sends cryptographic integrity proofs to the backend, ensuring that only genuine, untampered mobile clients running in secure environments can access sensitive services.
Integrating Mobile App Protection Across the SDLC
Security cannot be treated as a final checkbox prior to store submission. Achieving scalable mobile security requires a "Shift-Left" DevSecOps workflow:
- Threat Modeling and Secure Coding: Architect systems using secure storage (such as iOS Keychain and Android Keystore) and eliminate hardcoded credentials during early sprints.
- Continuous Static Analysis (SAST): Run automated scanners inside CI/CD pipelines to catch insecure dependencies, misconfigured permissions, and cleartext logging vulnerabilities before pull requests are merged.
- Automated Dynamic Testing (DAST) and MAST: Spin up automated test suites inside emulated and physical device test farms to monitor memory states, validate network transport security, and confirm SSL pinning integrity.
- Build-Time Binary Hardening: Inject deterministic RASP capabilities, control flow obfuscation, and anti-tamper logic directly into release builds.
- Automated Signing and Attestation: Sign the hardened artifact with verified certificates, ensuring seamless compliance with application store delivery requirements and enterprise registries.
- Post-Launch Threat Telemetry: Continuously monitor live threat streams to discover emerging exploitation attempts, tracking threat trends to inform iterative security updates.
A common misconception is that robust security must degrade app performance. If security initialization introduces startup delays or causes interface stuttering, users will abandon the product.
To maintain optimal user engagement:
- Protect Time-to-Interactive (TTI): Avoid executing heavy cryptographic checks or disk scans synchronously on the main thread during cold start. Security modules should initialize asynchronously or run on high-priority background worker threads to keep startup latency under two milliseconds.
- Schedule Workloads Responsibly: Stagger continuous environment integrity checks to prevent CPU spikes that cause frame drops or trigger Android Application Not Responding (ANR) warnings.
- Implement Battery and Resource Budgets: Restrict network telemetry uploads to batched, compressed background requests that avoid draining battery or thrashing cellular radios.
- Establish Graceful Degradation Modes: If a user device is running on low battery or constrained memory, the security runtime should switch to lightweight monitoring rather than degrading interface responsiveness.
Governance, Compliance, and Shared Responsibility
Modern mobile compliance requires aligning app defenses with recognized industry standards such as the OWASP Mobile Application Security Verification Standard (MASVS).
Whether building financial tools or deploying specialized healthcare app security solutions, organizations must prove to regulators and auditors that data remains protected at rest, in transit, and during execution.
Establishing the Mobile Security Shared Responsibility Model
Security is an interconnected lifecycle shared across developers, operations teams, and end users. Clear role demarcation ensures no single point of failure:
- Developer Responsibilities: Enforcing secure local storage, implementing zero-trust network encryption, obfuscating release binaries, adhering to least-privilege permissions, and conducting regular code reviews.
- Security Operations (SecOps) Responsibilities: Monitoring runtime threat telemetry feeds, managing automated CI/CD security pipelines, pushing regular security patches, and maintaining backend API authentication infrastructure.
- End-User Responsibilities: Applying timely operating system updates, maintaining strong biometric device credentials, avoiding unofficial app side-loading, and practicing basic physical device hygiene.
Selecting the Right Mobile App Protection Solution
When evaluating mobile protection platforms, engineering leaders should assess solutions across several operational criteria:
- Broad Platform and Framework Support: Look for native compatibility with Swift, Kotlin, React Native, Flutter, Cordova, and Unity to ensure consistent protection across diverse tech stacks.
- Low False-Positive Tolerance: Deterministic binary checks must reliably identify actual attacks while avoiding false positives on clean consumer devices, preventing unnecessary account lockouts.
- Resilient Telemetry and Scalability: Threat intelligence engines must ingest threat data at scale without generating excessive network overhead.
- Auditable Compliance Reporting: Solutions should provide clear, exportable audit trails that map directly to compliance frameworks, streamlining regulatory reviews.
Frequently Asked Questions About Mobile App Protection
How does RASP differ from standard code obfuscation?
Code obfuscation is a passive, static defense mechanism applied during the compilation phase. It scrambles class names, flattens execution logic, and encrypts strings to make the binary difficult for a human analyst or static decompiler to understand. However, once the application is running in device memory, obfuscation alone cannot stop an attacker from attaching a debugger or using dynamic hooking tools like Frida to manipulate variables in real time.
Runtime Application Self-Protection (RASP) is an active, dynamic defense mechanism. It monitors the app while it is executing, identifying real-time environment changes such as root cloaking, unauthorized memory alterations, and dynamic method interception. While obfuscation makes reverse engineering difficult, RASP actively detects attacks and shuts them down on the spot.
Can mobile app protection policies be applied without full MDM enrollment?
Yes. Modern Mobile Application Management (MAM) frameworks allow organizations to apply comprehensive data protection policies directly to individual apps without requiring full Mobile Device Management (MDM) enrollment. This architecture is ideal for Bring Your Own Device (BYOD) and contractor environments.
Under a MAM-only model, corporate data inside managed applications is encrypted, isolated from personal software, and subjected to strict access policies (such as copy/paste prevention and biometric requirements). The enterprise gains complete control over its business data—including the ability to perform remote selective wipes—without monitoring or accessing the user's personal applications, photos, or browsing history.
When implemented correctly using asynchronous workload scheduling and optimized binary injection, runtime shielding has virtually no noticeable impact on app performance. Advanced RASP implementations add less than two milliseconds to cold-start execution times.
By moving heavy integrity checks to background threads and off the main UI thread, applications preserve smooth 60-to-120 frame-per-second scrolling and immediate user interaction. Modern runtime governors also incorporate resource budgets that dynamically adjust inspection frequency during low-battery or memory-constrained states.
Future-Proofing Mobile Resilience Beyond the Perimeter
Protecting mobile applications requires moving beyond traditional perimeter thinking. In an environment where applications operate on unmanaged hardware and threat actors leverage automated tooling to compromise assets in under 30 minutes, passive defenses are no longer enough. Long-term mobile resilience demands a layered, proactive strategy combining deterministic binary hardening, active RASP defense, zero-trust API validation, and automated DevSecOps pipelines.
At Synergy Labs, we engineer secure, high-performance mobile and web applications designed to withstand modern threat environments. Our delivery framework pairs you with an in-shore CTO who guides technical architecture alongside an agile, elite offshore development team. We operate under a predictable fixed-budget model with transparent milestone-based payments, ensuring your applications launch rapidly, scale smoothly, and maintain enterprise-grade security from day one.
Whether you are designing a new digital product from scratch or hardening an existing enterprise portfolio, our team can help you build and protect your mobile ecosystem. Explore our end-to-end mobile app development and security services to start securing your digital products today.